The latest findings from NordLayer Intelligence by NordStellar, a threat exposure management platform, reveal that cybercrime-related discussions are increasingly shifting to Telegram. Across seven tracked cybercrime categories on Telegram and dark web forums, the platform’s unweighted average share of discussions reached 45% in the first five months of 2026.
Telegram’s share for January-May 2026 is 61% higher than its 28% share across the whole of 2025, signaling that cybercrime chatter on the platform is escalating quickly.
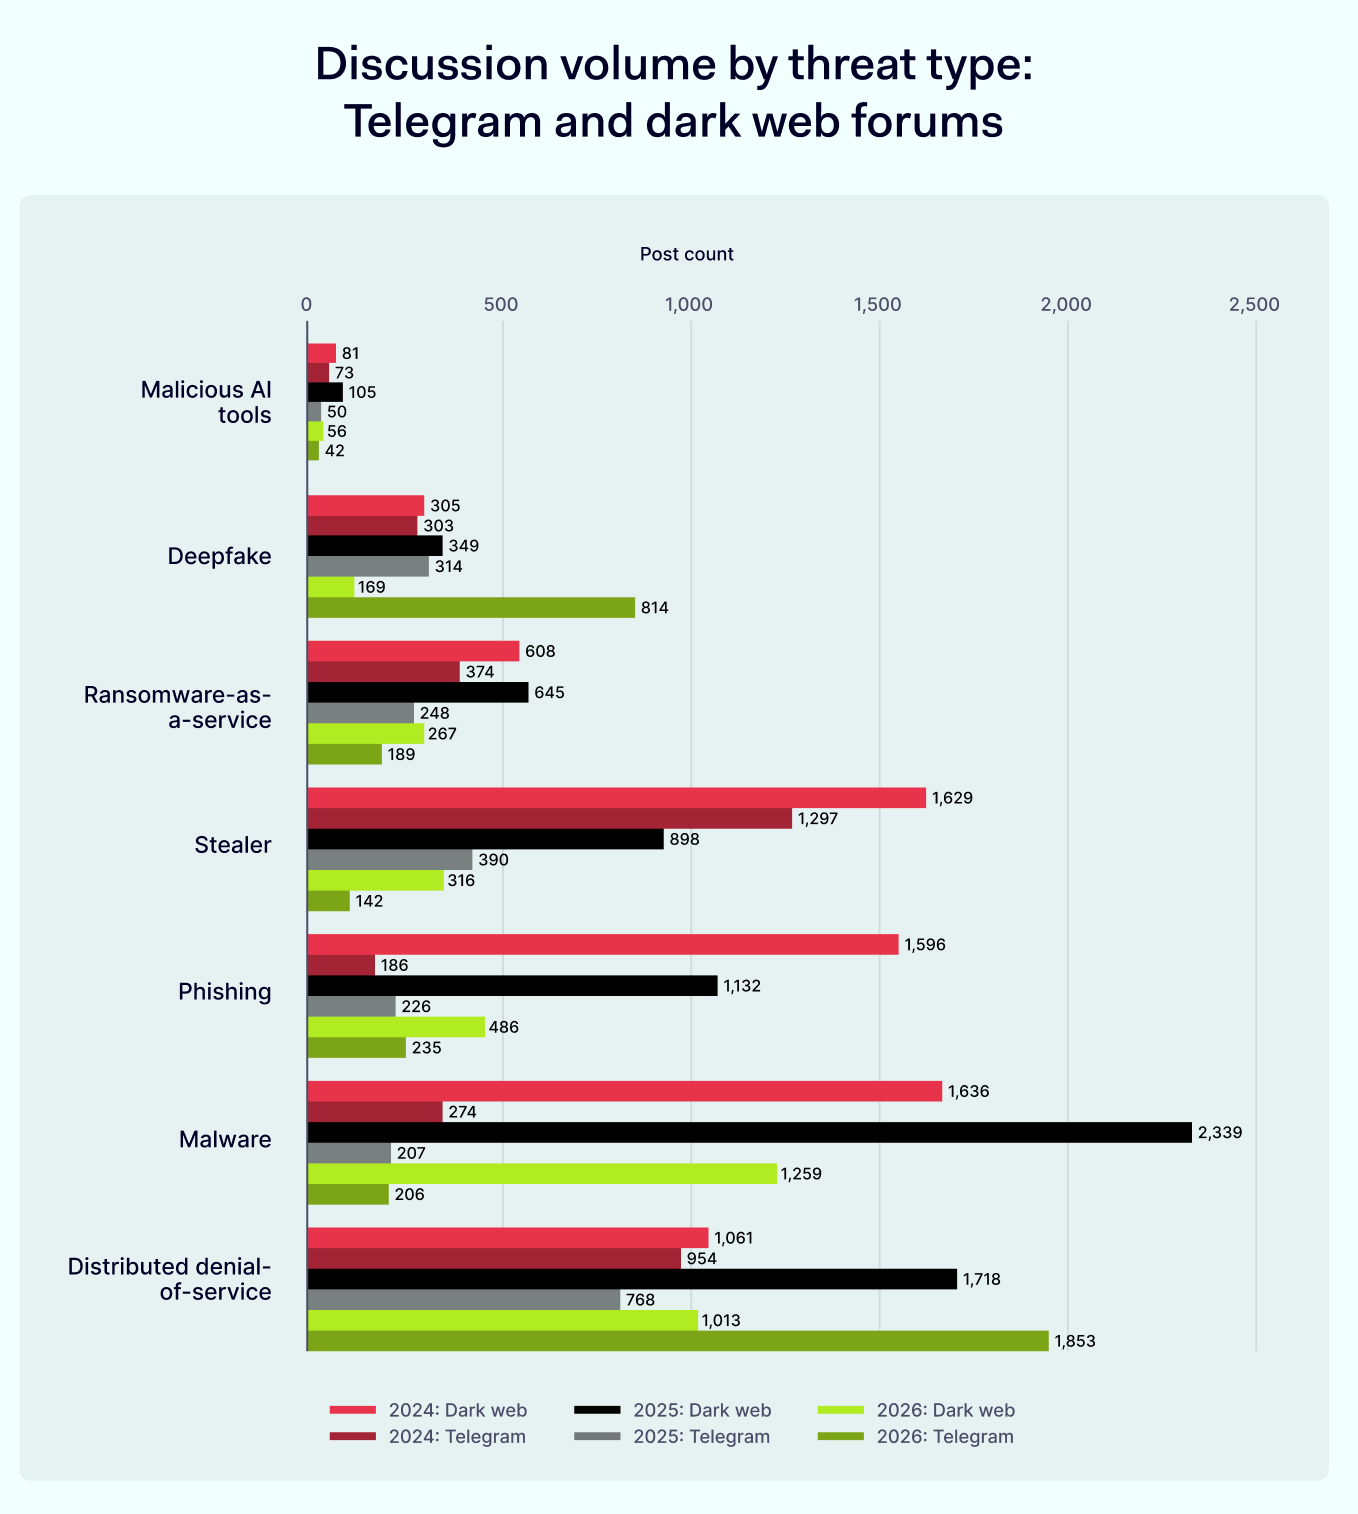
According to Vakaris Noreika, a cybersecurity expert at NordLayer Intelligence, one reason for the increase in cybercrime discussions on Telegram may be the relentless dismantling of traditional dark web forums by law enforcement. High-profile seizures of large hacker forums like LeakBase could have pushed threat actors to look for alternatives.
“Dark web forums are essentially communities for threat actors, and they spend years building their reputation to prove the trustworthiness of their sellers,” explains Noreika. “Each time a dark web forum gets taken down, it fragments the market. The threat actor community that used the forum then scatters across other smaller forums, where the once-trusted sellers enter as new, unverified users, and find it challenging to find new potential buyers.”
He explains that even after threat actors join a new dark web forum, they’re well aware that it could potentially meet the same fate.
“Building credibility, and even getting accepted into a new dark web forum, requires time and effort, and with the increasing likelihood of it eventually getting shut down, some threat actors might deem the investment no longer worthwhile,” says Noreika. “Telegram operates without these complex re-registration and reputation-building processes, making it the simpler alternative.”
A more accessible entry point for emerging threat actors
Noreika emphasizes that navigating the complex dark web infrastructure is no easy feat, especially for newcomers. Telegram, on the other hand, is a mainstream messaging platform that requires no special software or invitation to access.
“Compared with the dark web forums, Telegram presents a much lower-friction environment,” says Noreika. “Even though the platform blocked over 20 million groups and channels this year according to their official safety report, cybercriminals are quick to regroup, just as they have long done on the dark web, and doing so is far easier on Telegram.”
He suggests that the current Telegram cybercriminal ecosystem is most likely populated by newcomers who are searching for automated, mass-volume attacks to get their foot into cybercrime without the necessary skillset as well as more experienced hackers who use the platform to advertise their services or carry out lower-value deals while still keeping their main operations on the dark web.
“Despite the risks posed by ongoing law enforcement operations, the dark web offers higher operational security, and threat actors aren’t likely to trust Telegram for high-value transactions,” says Noreika. “The reputation and vetting infrastructure exists on the dark web for a reason — it’s unlikely that threat actors would carry out highly expensive and risky deals in a messaging platform that should cooperate with law enforcement.”
Staying on high alert for scalable attacks
According to Noreika, the findings of increasing cybercrime discussions on Telegram illustrate that cybercriminals are quick to adapt and are a reflection of the changes in the current cyberthreat landscape, which has experienced an influx of newcomers deploying low-skill, yet high-volume attacks.
“This shift doesn’t necessarily signal a wave of more sophisticated attackers, but a growing number of lower-skilled threat actors using easily accessible tools to launch high-volume campaigns,” says Noreika. “That means staying on high alert for threats such as phishing, credential theft, account takeover attempts, denial-of-service-for-hire activity, and deepfake-enabled fraud, all of which can be scaled quickly and deployed with limited technical expertise.”
He recommends users and organizations re-evaluate their cybersecurity hygiene, ensuring that they use unique passwords for all accounts and don’t store them in built-in browser password managers, and that multi-factor authentication is enabled wherever possible. Software and systems should be kept up to date with the latest patches, and publicly available personal information should be kept to a minimum to reduce the material that attackers can use for social engineering or deepfake creation.
“If cybercriminals manage to get a hold of credentials or other sensitive information, it’s crucial to act as soon as possible,” says Noreika. “Deep and dark web monitoring can provide alerts of many instances of leaked data, allowing for the detection of leaks across both Telegram and multiple dark web forums. This visibility is key to initiating urgent responses — such as changing passwords, revoking access from compromised accounts, and staying on high alert for any signs of further escalation.”
Methodology: Nordayer Intelligence analyzed monthly post counts across dark web forums and Telegram channels monitored by the NordLayer Intelligence platform, covering seven popular cybercrime categories from January 2024 to May 2026. Between January 2024 and May 2026, 86 dark web forums and 1,890 Telegram channels were monitored. As new sources emerged and others were shut down or seized during this period, year-on-year comparisons reflect changes in activity alongside shifts in the source pool itself. “Share” refers to the average proportion of posts across the seven tracked cybercrime categories, calculated by measuring Telegram’s share of posts in each category separately and then averaging those figures. 2026 figures cover January–May only.
Findings are limited to NordLayer Intelligence’s monitored sources and are not representative of all activity on Telegram or the dark web. Post counts measure discussion volume, not confirmed criminal activity or victims. Only aggregate counts were analyzed; no personal user data was collected. For more information, visit NordLayer Intelligence’s blog post.
Disclaimer: This analysis is provided for general information only and does not constitute legal, security, or professional advice, nor any guarantee of security or outcome. It reflects activity detected within NordLayer Intelligence’s monitored sources during the stated period and describes aggregate patterns only – no conclusion is drawn about any identified individual or organisation. References to third-party platforms and services are for identification and factual reporting only and do not imply any wrongdoing by, endorsement by, or affiliation with those parties. All third-party trademarks remain the property of their respective owners.


Guest Post: Fortune 500 not so fortunate: Employee credentials leak every 100 seconds
Posted in Commentary with tags NordLayer on September 25, 2026 by itnerdFindings from a report from NordLayer, a toggle-ready network security platform for business, reveal that credentials of Fortune 500 employees are being leaked on the dark web at an alarming rate, with the overall number of leaked credentials reaching nearly 10 million. The numbers are accelerating in 2026 — dated infostealer logs from this year show a new Fortune 500 credential appearing on the dark web every 100 seconds.
NordLayer analyzed findings from NordLayer Intelligence by NordStellar, a threat intelligence platform, which revealed that 9.96 million Fortune 500 employees’ credentials were leaked on the dark web. The research found that over 6.6 million unique corporate email addresses were exposed.
The leaked credential sets analyzed in the research comprise combolists — re-purposed credentials obtained from data breaches and infostealer infections — and dated infostealer logs, the only sets that record when the data was collected.
Analysis of infostealer logs shows that 130,000 Fortune 500 employee credentials were leaked on the dark web across roughly 147 days in 2026 alone. This amounts to a new Fortune 500 credential surfacing on the dark web every 100 seconds.
“The credential leaks that could be traced down to this year were harvested using infostealer malware,” says Andrius Buinovskis, cybersecurity expert at NordLayer. “Unlike ransomware, which typically targets specific organizations, infostealer campaigns are often more opportunistic, focusing on individual users rather than entire companies. This malware primarily hides within pirated software, gaming applications, fraudulent ads, fake captchas, and phishing emails.”
Almost all credentials harvested from browsers
According to Buinovskis, infostealers scrape data from users’ devices almost immediately after infection, stealing any credentials or credit card details they come across. The browser is their preferred hunting ground for users’ log-in information — of the analyzed 2026 infostealer logs that record a source application, 99% point to browsers.
“Infostealer malware is specifically designed to extract credentials from built-in browser password managers. Because standard browsers store this sensitive data in predictable local directories, it is an easy target for malware,” explains Buinovskis. “The vulnerability of these industry giants proves that even the best corporate defenses can be bypassed by a single employee’s habits. In the face of opportunistic malware, the browser has become the enterprise’s weakest link.”
Desk-heavy industries top infostealer exposure rates
2026 infostealer data analyzed in the research shows that mid-sized Fortune 500 companies record higher infostealer exposure rates than the largest employers. Companies in the mid-sized bands (between 5,000 and 25,000 employees) record the highest median credential leakage rate — 1.27 unique credentials per 1,000 employees — while the largest employers show the lowest rates. The highest per-employee credential leak rates come from mid-sized technology companies, topping out at 42 credentials per 1,000 employees.
By industry, media and entertainment companies show the highest median credential leakage rate at 10.59 per 1,000 employees, followed by telecommunications and technology at around 3. According to Vakaris Noreika, a cybersecurity expert at NordLayer Intelligence, the rates mirror the attack surface these industries expose — sectors where nearly every employee holds a corporate login and saves credentials in a browser present infostealers with more to harvest.
“Many Fortune 500 giants employ vast numbers of frontline staff — whether on factory floors or in retail outlets — who operate without a corporate inbox, naturally lowering the company’s overall credential footprint,” says Vakaris Noreika. “At the opposite end, companies operating in the media and entertainment, telecommunications, and technology industries are almost entirely desk based, meaning nearly every employee is a potential infostealer target — and that exposure accumulates fast.”
Safeguarding against infostealers
Buinovskis highlights five main measures companies should implement to build an infostealer-resistant cybersecurity strategy.
Methodology
NordLayer and NordLayer Intelligence by NordStellar analyzed leaked credentials and identified those tied to domains belonging to 2026 Fortune 500 companies, covering 500 companies and 3,692 corporate domains. Subsidiary brands were not included. The research began with 34.86 million raw records, which were deduplicated to 9.96 million unique email and password pairs, counted once per company. Each company was matched to its industry, revenue, and headcount. The leaked sets are made up of combolists and infostealer logs, and only the infostealer logs carry a collection date. About 130,000 of those dated records fall within roughly 147 days of 2026, which works out to about 1 new credential every 100 seconds. Per-employee exposure was calculated by dividing a company’s unique leaked emails by its headcount, then scaled to a rate per 1,000 staff and grouped by company size and by industry for comparison.
Leave a comment »