Archive for September 9, 2026

Microsoft Threatens Over “ShieldBreak”

Posted in Commentary with tags on September 9, 2026 by itnerd

Following Microsoft’s September 2026 Patch Tuesday security updates, a security researcher uncovered a new Microsoft Defender zero-day exploit named “ShieldCrash,” a bypass for the recently patched ShieldBreak Defender privilege escalation.

Ensar Seker, CISO at cybersecurity threat intelligence company SOCRadar, provided the following comments:

“ShieldCrash is concerning not simply because it affects Microsoft Defender, but because it appears to expose a recurring weakness in how this attack path has been remediated. When researchers can bypass successive fixes for RoguePlanet and ShieldBreak, it suggests the underlying security boundary or attack surface may require a more comprehensive redesign rather than another narrowly targeted patch.

It is important, however, to describe the current impact accurately. The publicly released proof of concept reportedly performs an arbitrary file read under the SYSTEM security context on fully patched Windows systems. That could expose highly sensitive files that an ordinary user cannot access, including configuration data, credentials or other secrets. Based on the information currently available, it does not yet provide an attacker with a full SYSTEM shell or arbitrary write capability. Nevertheless, privileged file disclosure can become an important component of a larger attack chain.

Organizations should not disable Defender as a reaction. Security teams should closely monitor Microsoft’s guidance and Defender intelligence updates, ensure tamper protection is enabled, restrict local execution and administrative access, and hunt for suspicious processes interacting with protected files through Defender-related mechanisms. Because proof-of-concept code is now public, defenders should assume attackers are examining it for ways to expand the primitive into credential theft, persistence or full privilege escalation. Microsoft should also assess the complete vulnerability class and related code paths, not only the specific condition demonstrated by this latest proof of concept.”

Microsoft responded with warnings of legal action against anyone engaging in “malicious activity causing real harm” to its customers, prompting many to believe that the company was directly threatening the security researcher.

But the fact is that the cat is out of the bag so to speak. Therefore Microsoft will need to deal with it. So lets see if they actually deal with it or not.

Parallel Works and CoreWeave to Accelerate DARPA Biological Research with Fully Managed AI Cloud Environment    

Posted in Commentary with tags on September 9, 2026 by itnerd

Parallel Works, Inc. and CoreWeave, Inc. today announced the deployment of a managed AI and high-performance computing platform for the Defense Advanced Research Projects Agency (DARPA) Network of Optimal Dynamic Energy Signatures (NODES) program.

The managed platform, delivered through Parallel Works’ ACTIVATE control plane and built on CoreWeave’s AI cloud platform, provides researchers with immediate access to the large-scale computing, orchestration software, and technical support required for advanced biological modeling and AI, without the delays and complexity of building and managing infrastructure.

The rapid adoption of AI is reshaping scientific research. Delivering AI cloud infrastructure, however, can take months, which can delay research and consume technical resources. By delivering a fully managed environment, Parallel Works and CoreWeave allow researchers to train AI models and run complex simulations within days rather than weeks or months.

NODES addresses complex challenges in the dynamics of biological systems, work that requires large-scale, dependable computing resources. Rapid access to dedicated GPU resources enables program performers to pursue simulation and modeling campaigns without delays associated with accessing and managing infrastructure.

Researchers access the environment through a single sign-on, with the ACTIVATE platform combining direct support, dedicated compute, unified orchestration and operational visibility:

  • End-to-end support: Parallel Works operates the environment for DARPA through its ACTIVATE platform, which handles user onboarding, identity and access, provisioning, scheduling, and reporting, with around-the-clock direct-to-expert support for both the platform and researcher applications.
  • Dedicated compute capacity: A dedicated reservation on NVIDIA HGX H100 systems, enterprise-scale storage, and high-speed NVIDIA Quantum InfiniBand networking. Parallel Works ACTIVATE divides the reservation across the NODES research teams, so each team holds a guaranteed allocation and can draw on shared capacity when it is available.
  • Unified orchestration: Parallel Works ACTIVATE enables DARPA researchers to access SUNK and CoreWeave Kubernetes Service (CKS) uniformly from a single platform. SUNK, CoreWeave’s Slurm on Kubernetes offering, enables researchers to run workloads of different kinds and sizes efficiently in the same underlying compute environment. ACTIVATE manages the accounts, allocations, and sharing policies that determine how the research teams use those resources.
  • Operational visibility: Parallel Works ACTIVATE provides the program and each research team usage and utilization reporting across the environment, while CoreWeave’s observability stack monitors the health of the underlying fleet, so issues are caught at the infrastructure layer before they cost time on a multi-week run.

More information on The Network of Optimal Dynamic Energy Signatures (NODES) program DARPA NODES can be found here: https://www.darpa.mil/research/programs/nodes
Other World Computing Expands USB4 Products Portfolio – Launches OWC USB4 Hub and USB4 40Gb/s Active Optical Cables in 3-Meter and 5-Meter Lengths

Posted in Commentary with tags on September 9, 2026 by itnerd

Other World Computing today announced the expansion of its USB4 product portfolio with the addition of the OWC USB4 Hub and USB4 40Gb/s Active Optical Cables in 3-Meter and 5-Meter Lengths.

The OWC USB4 Hub is designed for creative professionals, heavy storage users, and hybrid workers, as well as anyone using a modern laptop as their primary computer who wants full desktop connectivity without the clutter. With up to 40Gb/s of total bandwidth, one USB4 cable connects their laptop to fast external storage, accessories, and an HDMI 2.1 display while delivering up to 81W of charging – eliminating the constant juggling of ports, adapters, dongles, and chargers. In short, it gives users the portability of a laptop without connectivity compromises when they sit down to work.

OWC USB4 Hub Key Features:

  • One Cable Desk Setup: Up to 40Gb/s of total bandwidth, high resolution and high refresh rate display output, and industry leading charging, all through a single USB4 cable.
  • Blazing Fast USB4 Speed: Two USB4 ports deliver the performance to keep up with your workflow. Now you can simultaneously pull files from a card reader while using an SSD to back up files.
  • Native HDMI 2.1 Connectivity: With a built-in HDMI 2.1 port, customers can directly plug in any modern HDMI display up to 4K 120Hz, 4K 240Hz with DSC, or 8K 60Hz without adapters or dongles.1
  • Up to 81W Host Charging: The dedicated power supply delivers up to 81W through the USB4 host connection. Smart Power Delivery handles allocation between the laptop and connected devices automatically.2
  • Two 10Gb/s USB-C Ports: Two additional USB-C ports for drives, adapters, and accessories at speeds that won’t slow down your workflow.
  • Works With Everything: Compatible with Thunderbolt 5/4/3, USB4, and USB-C Mac, Windows, Linux, and iPad Pro hosts and devices.
  • Silent and Cool by Design: The fanless aluminum housing dissipates heat efficiently for quiet, throttle-free operation.

The OWC USB4 40Gb/s Active Optical Cables, now available in 3-meter and 5-meter lengths, are the fastest, most powerful, and reliable cost-effective solution for long distance Thunderbolt and USB4 connectivity. The cables deliver: 

  • NEW! DisplayPort Alt Mode Series Support: Compatible with both Thunderbolt displays and USB-C displays using DisplayPort Alt Mode. 
  • Placement Flexibility: Solves the longer distance connectivity needs of Thunderbolt 40Gb/s and USB4 devices by enabling optimal placement for a highly organized, convenient, quieter, and productive workspace. Longest reach in the lineup at up to 16 feet (5m model).
  • Uncompromised Speed: Work and play faster with up to 40Gb/s of stable data transfer speed over long distances.
  • Versatile Connections: Connect to externally powered Thunderbolt 40Gb/s and USB4-equipped docks/hubs, displays, eGPUs, PCIe expansion, RAID storage, and more.
  • Power: Lab-certified for safe power delivery from Thunderbolt and USB-C devices that provide power delivery to a host machine.
  • Diverse Displays Compatibility: Supports high-resolution Thunderbolt displays up to 8K, including Apple Pro Display XDR, Apple Studio Display, LG Ultrafine, and other Thunderbolt-based displays. DisplayPort Alt Mode Series cables also support USB-C displays using DisplayPort Alt Mode. 
  • If It’s Lit, You’re Legit: Features LED indicators on both ends that confirm your connection status at a glance.
  • Premium Reliability: Braided nylon exterior over advanced internal fiber optical cable for highly durable and consistent signal reliability; immune to EMI/RFI interference.

The OWC USB4 Hub will be generally available (GA) at the end of October and priced at $129.99. To learn more and pre-order, please visit: https://www.owc.com/solutions/usb4-hub. 

The OWC USB4 40Gb/s Active Optical Cables will be generally available (GA) in mid-October in 3-meter and 5-meter lengths, and priced at $98.99 and $129.99, respectively. To learn more and pre-order, please visit: https://www.owc.com/solutions/usb4-cables. 

The industry will have the opportunity to see the new OWC USB4 Hub and USB4 40Gb/s Active Optical Cables in 3-meter and 5-meter lengths during the International Broadcasting Convention, IBC 2026, taking place September 11-14, at RAI Amsterdam, in Hall 7, OWC Booth 7.A60.

82% of Canada’s top AI companies won’t say how long they keep your data says Cybernews

Posted in Commentary with tags on September 9, 2026 by itnerd

New research from Cybernews’ 2026 AI Trustworthiness Ranking reveals a transparency gap among Canada’s leading AI companies: 82% won’t clearly disclose how long they retain user data, and 59% don’t say whether that data is used to train their AI models.

Cybernews has published its ranking, evaluating 500 AI companies across 36 countries on security, data privacy, transparency, and public perception. As part of the project, the team rated 17 leading Canadian AI companies.

Key findings:

  • According to the Cybernews AI Trustworthiness Ranking, Canadian AI companies scored an average of 64 out of 100.
  • 82% of leading Canadian AI companies do not clearly disclose how long they retain user data.
  • 59% of top Canadian AI companies do not clearly disclose whether they use user data to train AI models.
  • Transparency was Canada’s strongest area, with an average score of 92, while security was the weakest at 28.
  • Vidyard ranked first in trustworthiness, followed by Ideogram, Spellbook, LANDR, and Thomson Reuters.

You can explore the full AI Trustworthiness Ranking and individual company scores here: AI Trustworthiness Ranking 2026

Silent Push 6.1 Platform Detects Attacker Infrastructure Earlier for Preemptive Action  

Posted in Commentary with tags on September 9, 2026 by itnerd

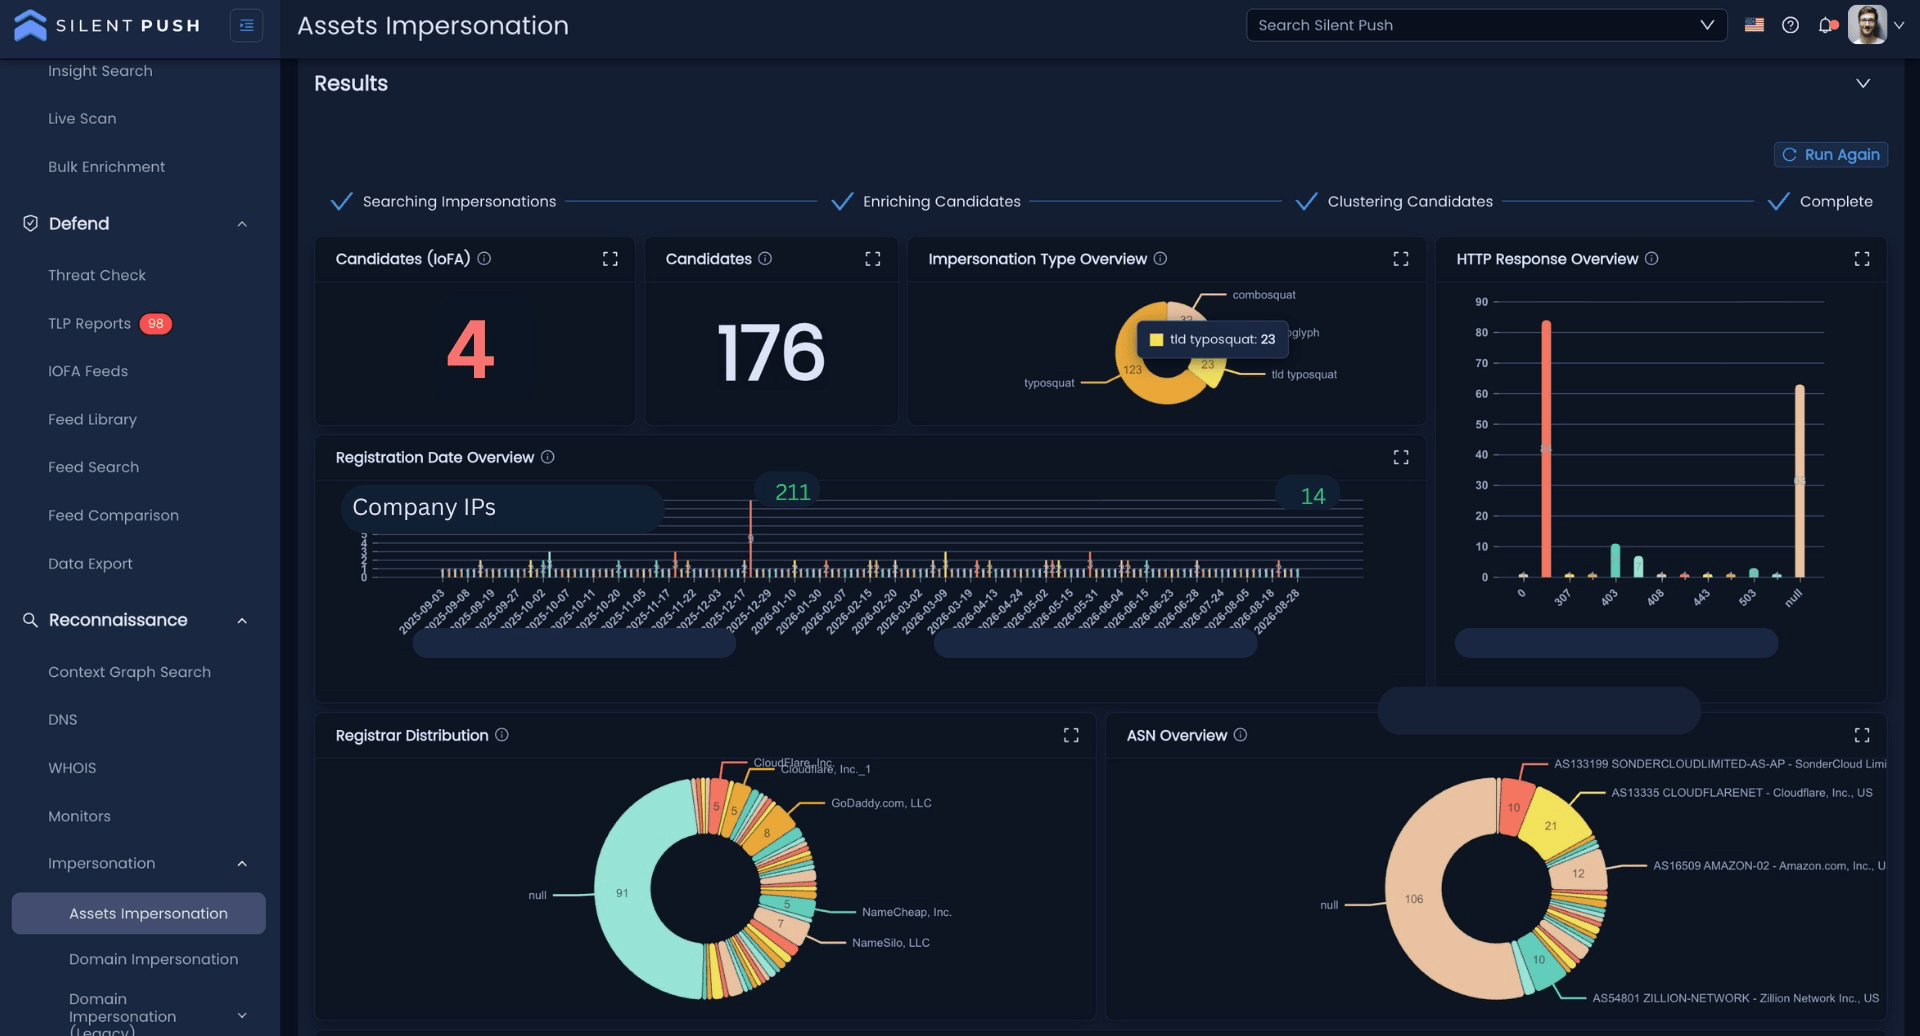
Silent Push today announced enhancements to its preemptive cyber defense platform with Silent Push 6.1. The latest version features a complete rebuild of its Brand and Infrastructure Impersonation capabilities, now fully automated so the platform continuously hunts for imposters and keeps customers informed of what it finds on their behalf, and enhanced extensibility to enable analysts to seamlessly integrate into security telemetry and AI tools for faster pivots, and controlled intelligence delivery.

Brand and infrastructure impersonation is now a formal intelligence requirement, not just a marketing concern. Companies are being forced to know what malicious domains, phishing assets, or impersonation campaigns are being used against their brand, and how they can stop them at scale.

Silent Push 6.1 is built to answer that question before the first phishing email is sent. Set it once, and the platform keeps finding new look-alike domains and reporting them to your team on an ongoing basis.

Silent Push 6.1 centers on protecting what matters to organizations and accelerating everything analysts do next. The platform meets analysts where they already work: SOAR platforms, browsers, AI tools, and threat-intel feeds, further shortening the distance between finding threats and acting on them.

New capabilities include:

  • Next-Gen Brand and Infrastructure Impersonation: One of the most direct threats an organization faces is brand and infrastructure impersonation, and 6.1 rebuilds how Silent Push detects it. Configure your brands and assets once, and the engine continuously finds look-alike domains, scores them by risk, enriches them with registrar and hosting context, clusters them by threat actor, and alerts your team with takedown-ready evidence.
  • Advanced Pivot Control: Displays existing Silent Push data and lets you move into WHOIS or open-directory lookups without losing your place in the investigation. Insight Search now understands domains, IPs, ASNs, subnets, and HTML titles in a single query. Total View adds a PADNS timeline, IP certificates, one-click PDF export, and date filtering for screenshots.Ecosystem Reach: With 6.1, the My Assets feature lets you build a reusable list of the infrastructure you own (domains, IP ranges, ASNs, and TLDs), tag it, and reuse it as a one-click input everywhere in the platform.
  • Integrations:
    • Palo Alto Cortex XSOAR: Silent Push intelligence is available inside XSOAR for automated playbooks and response workflows.
    • Chrome Extension: Investigate domains and indicators directly from the browser, without leaving the page you are on.
    • MCP Server: Exposes Silent Push data to AI assistants and agentic workflows over the Model Context Protocol (MCP).
    • Updated TAXII Server: Now supports bidirectional sharing, enabling two-way threat-intelligence exchange over STIX/TAXII.
  • TLP Amber Reports: Custom Silent Push analyst reports now support TLP: AMBER+STRICT, so exclusive, subscription-based intelligence reaches only the organizations and individuals meant to receive them.
  • Internationalization: The interface is now available in Korean and Spanish alongside English, with navigation and guidance fully localized per user, while the underlying data stays the same. Japanese will be available shortly, with additional languages available on customer request.
  • About Silent Push
  • Silent Push is the preemptive cyber defense company. It is the first and only solution to provide a complete view of emerging threat infrastructure in real time, exposing malicious intent through its Indicators of Future Attack® (IOFA) data, enabling security teams to proactively block hidden threats and avoid loss. The Silent Push standalone platform is also available via API, integrating with various security tools, including SIEM & XDR, SOAR, TIP, and OSINT, providing automated enrichment and actionable intelligence. Customers include some of the world’s largest enterprises within the Fortune 500 as well as government agencies. 

A free Community Edition is available.