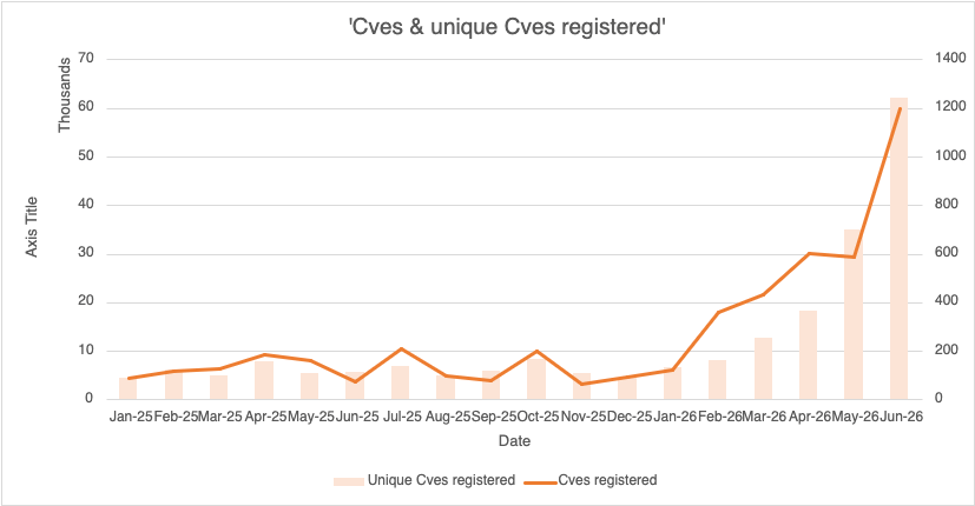
Recast tracks CVE disclosures for third-party applications through its Setup Store catalog. Since March 2026, the number of unique CVEs registered each month has climbed from roughly 150-200 to more than 60,000 in June alone. This trend lines up with major software vendors (Chromium, Firefox among them) adopting AI-assisted vulnerability testing.
Tuukka Tiainen serves as Senior Security Engineer at Recast Software, bringing over a decade of experience in IT and information security. His expertise spans technical security as well as governance, risk, and compliance. Passionate about threat and vulnerability management, Tuukka also brings deep knowledge of Microsoft’s security solutions.
His Bio is here and here is his LinkedIn profile: .
What’s driving the trend?
This trend is driven by the industry with the assumption that with the expended usage of the AI tools, vendors can test more and catch more vulnerabilities in their software.
I can only talk about what I’ve seen during the time I have reviewed the monthly statistics (since May 2024). It is visibly clear that something has changed in the number of unique vulnerabilities patched by vendors this year. You can see those spikes starting to grow in March this year.
Browsers: Chromium and Firefox have dominated the vulnerabilities number wise for the last three months. Both Mozilla and Google are participating in Project Glasswing, giving them access to Anthropic’s frontier AI model. Firefox is evidence that harnessing Claude Mythos in their pipelines has greatly increased the number of security bugs found. See the blog written by their Tech Lead and Principal Engineer.
Microsoft and Google haven’t disclosed similar information about the findings to public but at least Microsoft has admitted publicly that they use Mythos. There’s a pretty strong assumption that the reason is the same for them resulting in more patched vulnerabilities in the last few months. I think that the Project Glasswing is just the first wave. Once the model and other frontier models get into the hands of more software vendors it will result in even more vulnerabilities to be patched.
What are the operational or security implications? What should organizations be doing differently as a result?
By following the same narrative, organizations using the 3rd party software should have more vulnerabilities to deal with. I would even claim that the number of exploits will grow because AI has become so much better in autonomously discovering weaknesses and chaining multiple lower-severity issues into exploits. In the worst-case scenario there will be more of everything: vulnerabilities, software versions (patches), out-of-band patches, exploits and zero-day vulnerabilities.
Another big aspect of this is the patch gap possibly becoming the most important vulnerability management metric. The “patch gap” is the time between a security patch becoming available and it being installed on your systems. The industry has traditionally focused on zero-days, but the patch gap may become an equally important security challenge. If AI can help attackers quickly reverse engineer patches and understand the vulnerabilities they fix, the window between a patch being released and an exploit becoming available could shrink dramatically. In that world, the greatest risk is not necessarily the vulnerability no one knows about, but the one everyone knows about and hasn’t patched yet. If this is the case, patch management vendors need to help to minimize the time between a software vendor releasing a patch, making it available for the customers and customers actually applying the patch on their systems.
If organizations need to patch more and faster, it might become a heavy burden for IT and security. I think this is one of the reasons why, for example, CISA is driving its new initiative for patching. Check out Patch Smarter, Not Harder. I also wrote a blog over a year ago how to patch smarter based on other factors than just the good old CVSS.
According to CISA, only the most critical vulnerabilities should be patched within three days. It is up to organizations to come up with their own processes, but it will be even more important to be able to prioritize in the future. Organizations should also play with the idea that they must be able to effectively patch a vulnerability within three days. How does that change the existing practices and models?
A brief explanation of where the data came from, how it was collected, what timeframe it covers, and approximately how many applications/CVEs were analyzed.
The vendors report CVEs when a new version is published. Sometimes this information is added later (a few days). We (Recast) scan those resources and as soon as the CVE data is available, it is added to the Setup Store. We are collecting the data about the applications stored in the catalog. The trend started to take a clear shape from March 2026 on.
Are all these applications in Setup Store? Just third-party apps? Enterprise apps? Does the data include severity (Critical/High/etc.)?
This is related only to the applications stored in the Setup Store, so the scale in the market is larger. Those are 3rd party applications that were eligible to be added to the catalog. The data does not include the severity.
What is the biggest or most surprising trend?
It’s not that it’s surprising but rather expected. It is confirmation of the global security changes written in the data and that AI tools are used extensively and vendors are focusing on improving.
Here’s some raw data in graph form for your viewing pleasure:


Recast Expands Right Click Tools to Deliver Greater Application Visibility, Cloud-First Management, and Stronger Security
Posted in Commentary with tags Recast on November 5, 2026 by itnerdRecast today announced a series of Right Click Tools enhancements. Managing applications is getting harder as endpoints become more distributed and increasingly operate beyond the corporate network. Recast’s latest Right Click Tools capabilities bring application visibility, vulnerability insights, patching, and remote management together to help IT teams understand what’s running across their endpoints, identify risk, and take action wherever those devices are located.
These enhancements extend across environments managed with Microsoft Intune, Microsoft Configuration Manager, or a combination of the two, giving IT teams a more consistent way to manage applications across their evolving endpoint estate. Developed in collaboration with existing customers, the capabilities continue Recast’s investment in practical tools that meet organizations where they are today while helping them build a more proactive endpoint management strategy.
Expanded management for remote and cloud-only devices
Right Click Tools now removes more barriers to managing devices wherever they’re located. The Agent Gateway enables internet-based enrollment and remote management, helping teams reach endpoints that are not consistently connected to a corporate network. This enables administrators to investigate and address device issues remotely without having to coordinate with the end user to manage their device.
Greater application visibility and stronger patching
New and expanded inventory awareness from Right Click Tools Insights helps IT teams understand which applications are installed across their environments and where outdated versions may create risk. By bringing this visibility together with patching workflows, Right Click Tools Patching enables teams to move from discovering issues after they affect users to identifying and addressing gaps earlier.
Right Click Tools Patching keeps environments secure by identifying outdated application versions and applying updates to targeted devices. The latest version adds support for both ARM64 and macOS applications, extending centralized application maintenance to a broader mix of endpoints.
These visibility and patching capabilities are critical as the window for responding to application vulnerabilities continues to shrink. Recast’s proprietary database tracked a 438% increase in Common Vulnerabilities and Exposures (CVEs) and a 44% increase in the number of software versions released from the first quarter of 2026 to the third. Faster vulnerability discovery makes timely application inventory, prioritization, and patching increasingly important for endpoint teams.
Detailed release notes can be found on Recast’s website.
Leave a comment »