Archive for August, 2026

A phishing-as-a-service platform now uses AI voice agents posing as “Apple Support” to unlock stolen iPhones, for under 10 cents a call 

Posted in Commentary with tags on August 26, 2026 by itnerd

Researchers identified AnonyMousKIT, a phishing-as-a-service platform built to bypass Apple’s Activation Lock on stolen devices, using AI voice agents (all posing as “Alice from Apple Support,” running on the commercial Vapi voice platform in English, Spanish, and Portuguese) to trick victims into handing over passcodes, Apple ID credentials, and two-factor codes, information Apple says it never asks for. 

You can find more details here: AnonyMousKIT PhaaS uses voice AI agents to phish iPhone passcodes

Gidi Cohen, CEO & Co-Founder, Bonfy.AI:

“The real story here isn’t that AI can impersonate Apple Support convincingly, it’s how cheap that’s become. $0.096 a call gets you a voice agent that can run the whole script in three languages: ask for the passcode, then the Apple ID, then a live 2FA code. That used to take a skilled scammer sitting on the phone. Now it’s a rented service with published pricing and customer support. AI didn’t invent this scam, it just took the labor cost out of it, and that changes who can run one and how many they can run at once.

It’s also a good reminder that the backend behind these operations is usually way messier than the polished lure emails suggest. Researchers got into months of call logs, transcripts, and persona configs because of two exposed file paths, not some clever hack. Even the people running these platforms don’t seem to have much visibility into their own exposure.

But the part worth actually worrying about isn’t stolen phones, it’s what happens when this same trick gets pointed at employees instead of consumers. Cheap, real-time voice AI means help-desk calls, vendor calls, password-reset calls are all about to get a lot harder to sniff out just by listening. If a fake “Apple Support” agent can talk someone out of a 2FA code for pennies, the same setup works just as well faking IT support to get into a company. Security teams need eyes on how AI is being used against them, not just how it’s being used inside their own walls.”

Apple users need to be alive to this threat along with many other threats. Because there will always be a new threat that users need to keep their eyes out for.

Cyberattack disrupts Boston Scientific’s global operations and customer shipments

Posted in Commentary with tags on August 26, 2026 by itnerd

Medical device manufacturer Boston Scientific said it is experiencing a global operational disruption after detecting a cyberattack on August 25.

The incident has restricted access to information systems and business applications used across the company, including systems needed to process and ship customer orders. Boston Scientific said the disruptions are expected to continue while recovery efforts are underway, and it does not yet have a timeline for full restoration.

In Ireland, staff at its Cork facility were sent home Tuesday, and employees able to work remotely were subsequently instructed to do so. 

Jacob Krell, Senior Director: Secure AI Solutions & Cybersecurity, Suzu Labs:

   “A cardiac device that misses its ship date can mean a cancelled surgery. That’s what makes a company like Boston Scientific such an attractive extortion target. The attacker doesn’t need to destroy anything. They just need to make downtime more expensive than whatever they’re asking for.

   “Medical devices also aren’t something a hospital can always swap out at the last minute. Physicians have selected specific devices, patients are scheduled, inventory is already in place, and procedures have been planned around them. Disrupt order processing and shipping and the consequences show up in hospitals pretty quickly.

   “The harder problem is getting manufacturing back online. These aren’t ordinary IT systems. Software involved in producing and tracking FDA-regulated devices sits inside a validated quality system. Restoring a server is one thing. Establishing that the data coming out of that system can still be trusted is another.

   “You can’t ship something that gets implanted in a human body on trust alone. If production or quality systems were affected, Boston Scientific may have to establish that records are intact and trustworthy before normal operations resume.

   “That’s why employees at Boston Scientific’s manufacturing facility in Cork, Ireland being sent home matters. This isn’t just people losing access to email. The company has already confirmed disruption to order processing and shipping, and Cork shows that disruption reaching manufacturing operations. If quality or production data was also affected, getting the servers running could be the easy part.”

Damon Small, Board of Directors, Xcape, Inc.:

   “When a cyberattack halts order fulfillment and logistics across a global enterprise, an IT security incident becomes an immediate revenue and medical supply chain crisis. Because details regarding the initial attack vector remain sparse, it is not possible to recommend specific preventive technical steps for other organizations. That said, cybercriminals are often opportunistic and exploit vulnerable systems as soon as they discover them; it is currently unknown whether this was a targeted attack or just bad luck. Regardless of the entry point, disruption to core business applications forces defensive network isolation to stop lateral movement.

   “To maintain operational continuity during an ongoing intrusion, security teams must enforce strict logical boundaries between corporate administrative networks and fulfillment environments, maintain immutable offline backups, and regularly validate manual failover protocols.

   “Critical Takeaways:

  • When enterprise applications stall, cyber incidents rapidly escalate from IT disruptions to severe supply chain and revenue crises.
  • Attack vectors remain unconfirmed because threat actors frequently exploit opportunistic vulnerabilities rather than executing targeted campaigns.
  • Maintaining operational continuity requires enforcing strict network segmentation between administrative and fulfillment environments before an incident occurs.

   “Whether hit by targeted sophistication or bad luck on an unpatched system, the operational result remains the same without proper segmentation.”

Medical devices are the next frontier in terms of threat actors pwning organizations. I hope that all medical device companies are paying attention to this situation.

UPDATE:  Jeremy Leasher, Forward Deployed Security Architect, Binalyze Had This To Say:

“Boston Scientific appears to be the latest scalp for hackers targeting the healthcare industry, with many crucial suppliers and manufacturers affected in the past year or so.

“The fact that international staff have been told to work from home and offices have been shut suggests this may not be a simple smash-and-grab attack. It doesn’t appear to be about data but about stopping the business’ ability to provide its services. What we are likely to find out once the dust settles, is that the attack was predicated on some existing known security gap or flaw, and that the attacker’s initial entry is probably tied to some user or entity based credential that was exposed.

“This is another proof that the lines between types of cyberattack have essentially been wiped away. While we don’t know who’s behind it, affecting a medical company’s ability to supply things like pacemakers and stents is quite literally a matter of life and death for patients. 

“Speed is everything for attacks like this. Investigation can’t be an afterthought, organisations need to know if the attackers are still inside systems, which systems were affected and how attackers got in. The faster those questions are answered, the faster you can begin recovery and ensure an appropriate response.”
Volvo Car Canada Ltd. Appoints Director of Digital

Posted in Commentary with tags on August 26, 2026 by itnerd

Volvo Car Canada Ltd. is pleased to announce the appointment of Narcis Tajvidi as Director, Digital.

Currently serving as Online Business Lead, Narcis has played a pivotal role in advancing Volvo Car Canada’s digital business and customer experience strategy since joining the company in 2021, helping drive improvements across e-commerce, digital performance, retailer engagement, and omnichannel customer journeys.

With more than 15 years of leadership experience in the automotive industry, Narcis brings a strong combination of commercial, digital, and transformation expertise gained through progressive roles at both Volvo Car Canada and BMW Group Canada.

In her new role, she will lead the Digital, Data, and Technology portfolio for the market in Canada, with a focus on accelerating growth, strengthening customer and retailer experiences, advancing AI and data capabilities, and ensuring technology investments deliver meaningful business value.

Recognized for her collaborative leadership, Narcis is committed to building strong partnerships across retailers, colleagues, and global teams as the company continues its digital transformation journey.

BreachLock Unveils Breach360

Posted in Commentary with tags on August 26, 2026 by itnerd

BreachLock today introduced Breach360™, its agentic AI-powered autonomous penetration testing solution. Breach360 helps organizations continuously validate security controls, prove exploitability, and prioritize remediation across modern attack surfaces.

Breach360 brings autonomous penetration testing to the BreachLock Unified Platform, joining its Attack Surface Management (ASM) and Penetration Testing as a Service (PTaaS) solutions. This milestone makes BreachLock the only offensive security provider unifying continuous ASM, certified, expert-led penetration testing, and autonomous penetration testing in a single workflow. Security teams can now discover what’s exposed, validate what’s genuinely exploitable, and continuously test what matters most, informed by intelligence from more than 40,000 real-world penetration testing engagements and trusted by over 1,200 organizations worldwide.

Breach360 directly addresses a growing industry challenge: disconnected tools and alerts that provide little clarity about what is truly exploitable. Rather than generating another list of vulnerabilities, Breach360 validates real attack paths, confirms exploitability with documented evidence, and provides prioritized guidance on where organizations should focus remediation efforts.

Breach360 brings production-safe autonomous penetration testing across both web and network environments into a single experience, giving organizations a unified view of exploitable risk across their attack surface. Security teams can continuously validate both application and infrastructure security without managing disconnected tools.

Key Capabilities of Breach360

  • Autonomous Penetration Testing powered by agentic AI trained on intelligence from more than 40,000 real-world penetration tests.
  • Proof of Exploitability, helping teams focus on validated risk instead of false positives.
  • Unified Web and Network Pentesting Coverage, enabling continuous validation of infrastructure and application attack surfaces through a single solution.
  • Threat-Informed Security Validation aligned with real-world attacker behavior and MITRE ATT&CK techniques.
  • Real-Time Attack Path Visibility, allowing organizations to observe how vulnerabilities can be chained together to create business risk.
  • Production-Safe Autonomous Testing, with lateral movement and exploitation approvals, scope controls, guardrails, and kill-switch capabilities.
  • Optional Human-Verified Results, allowing organizations to add a certified BreachLock pentester as a final review checkpoint for findings and recommendations.
  • Prioritized Mitigation Guidance based on attacker logic and exploitability, not vulnerability scores alone.
  • Executive and Technical Reporting that transforms security findings into actionable remediation plans and board-ready insights.

Breach360 ensures that autonomous penetration testing does not mean giving up control. Security teams define scope, approve sensitive actions, set engagement parameters, and maintain oversight throughout the testing lifecycle. For teams requiring additional assurance, Breach360 offers optional expert review from certified BreachLock pentesters, combining the speed of autonomous execution with the accountability of certified, in-house penetration testing experts.

The launch of Breach360 reflects BreachLock’s continued investment in offensive security innovation and its vision for a future where organizations can continuously validate security controls through intelligent, scalable, and threat-informed testing.

Breach360 is available immediately through the BreachLock Unified Platform. For more information or to schedule a demo, visit www.breachlock.com.

Today Is Women’s Equality Day

Posted in Commentary with tags on August 26, 2026 by itnerd

Since 1971, Women’s Equality Day has been recognized every August 26, marking the anniversary of the certification of the 19th Amendment and women gaining the right to vote.

We’ve come a long way since then… But when you look at the tech industry, it’s pretty clear we still have work to do. Women make up just about a quarter of the global tech workforce. And while we talk a lot about getting more women interested in tech and bringing more women into the industry, experts argue that we need to talk just as much about what happens after they get here. Half of women in tech leave the industry by age 35. So, you can recruit all the talent in the world, but if people don’t see an opportunity to grow, contribute, lead, and build a career, you haven’t solved the problem.

Estelle Azemard, CEO of Leaseweb Canada, commented, “Today, just 26.7% of the global tech workforce are women. That’s not an opinion — it’s a fact, and it’s the result of decades of education, social conditioning, and systems that we all, women included, sometimes reproduce without realizing it. Equality isn’t women’s responsibility alone. It’s everyone’s work — men and women together.” 

To her point… It’s on all of us. Companies need to look at the opportunities they’re creating, the people they’re developing, and the culture they’re building – are we giving talented people a reason to stay? Are we listening to them? Are we giving everyone the chance to take on bigger challenges and become leaders?

Getting more women through the door matters. But that’s only the beginning. Hard skills and soft skills don’t belong to one gender, one race, one religion, or one background. They’re developed through learning, experience, and opportunity. 

The best companies recognize that talent can come from anywhere… and then make sure that talent has every opportunity to succeed.

Guest Post: Cybercrime chatter on Telegram gains momentum in 2026, new research finds

Posted in Commentary with tags on August 26, 2026 by itnerd

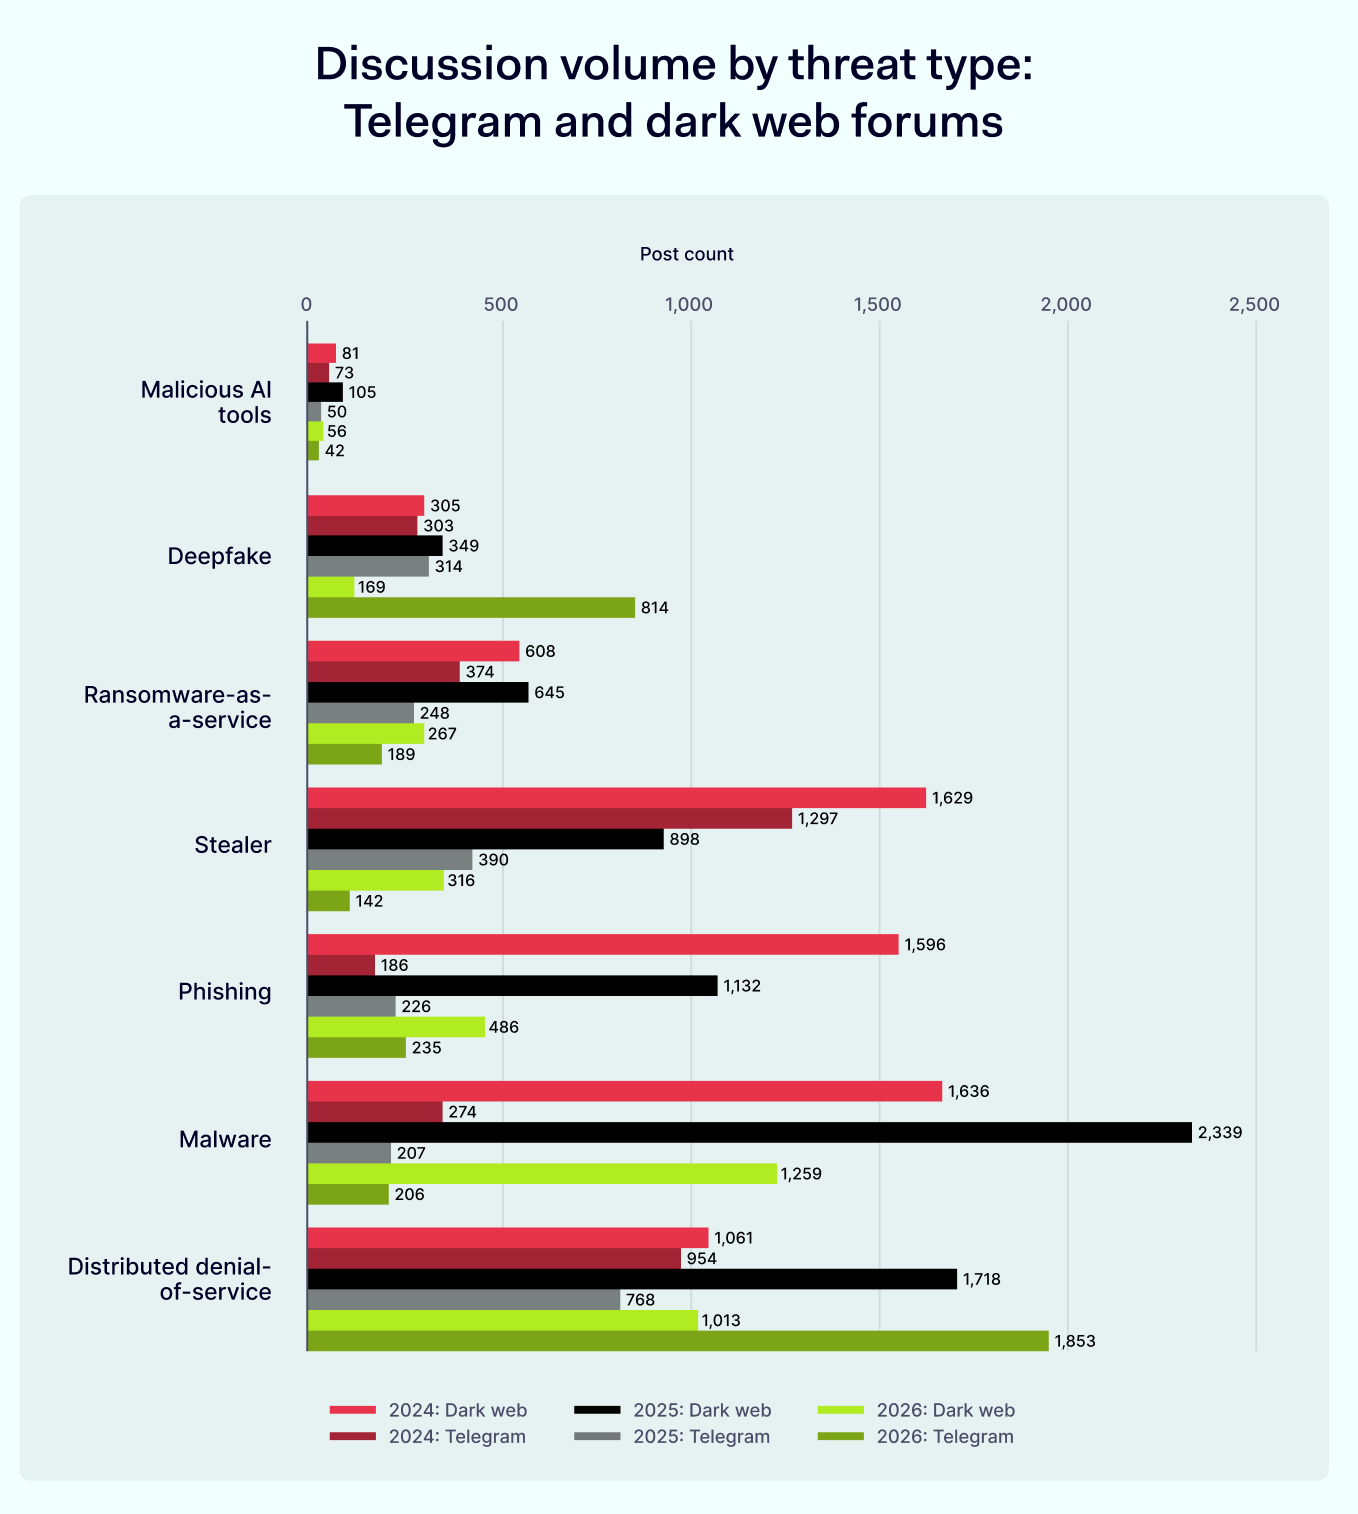
The latest findings from NordLayer Intelligence by NordStellar, a threat exposure management platform, reveal that cybercrime-related discussions are increasingly shifting to Telegram. Across seven tracked cybercrime categories on Telegram and dark web forums, the platform’s unweighted average share of discussions reached 45% in the first five months of 2026.

Telegram’s share for January-May 2026 is 61% higher than its 28% share across the whole of 2025, signaling that cybercrime chatter on the platform is escalating quickly. 

According to Vakaris Noreika, a cybersecurity expert at NordLayer Intelligence, one reason for the increase in cybercrime discussions on Telegram may be the relentless dismantling of traditional dark web forums by law enforcement. High-profile seizures of large hacker forums like LeakBase could have pushed threat actors to look for alternatives. 

“Dark web forums are essentially communities for threat actors, and they spend years building their reputation to prove the trustworthiness of their sellers,” explains Noreika. “Each time a dark web forum gets taken down, it fragments the market. The threat actor community that used the forum then scatters across other smaller forums, where the once-trusted sellers enter as new, unverified users, and find it challenging to find new potential buyers.” 

He explains that even after threat actors join a new dark web forum, they’re well aware that it could potentially meet the same fate. 

“Building credibility, and even getting accepted into a new dark web forum, requires time and effort, and with the increasing likelihood of it eventually getting shut down, some threat actors might deem the investment no longer worthwhile,” says Noreika. “Telegram operates without these complex re-registration and reputation-building processes, making it the simpler alternative.” 

A more accessible entry point for emerging threat actors

Noreika emphasizes that navigating the complex dark web infrastructure is no easy feat, especially for newcomers. Telegram, on the other hand, is a mainstream messaging platform that requires no special software or invitation to access.

“Compared with the dark web forums, Telegram presents a much lower-friction environment,” says Noreika. “Even though the platform blocked over 20 million groups and channels this year according to their official safety report, cybercriminals are quick to regroup, just as they have long done on the dark web, and doing so is far easier on Telegram.”

He suggests that the current Telegram cybercriminal ecosystem is most likely populated by newcomers who are searching for automated, mass-volume attacks to get their foot into cybercrime without the necessary skillset as well as more experienced hackers who use the platform to advertise their services or carry out lower-value deals while still keeping their main operations on the dark web.

“Despite the risks posed by ongoing law enforcement operations, the dark web offers higher operational security, and threat actors aren’t likely to trust Telegram for high-value transactions,” says Noreika. “The reputation and vetting infrastructure exists on the dark web for a reason — it’s unlikely that threat actors would carry out highly expensive and risky deals in a messaging platform that should cooperate with law enforcement.” 

Staying on high alert for scalable attacks

According to Noreika, the findings of increasing cybercrime discussions on Telegram illustrate that cybercriminals are quick to adapt and are a reflection of the changes in the current cyberthreat landscape, which has experienced an influx of newcomers deploying low-skill, yet high-volume attacks. 

“This shift doesn’t necessarily signal a wave of more sophisticated attackers, but a growing number of lower-skilled threat actors using easily accessible tools to launch high-volume campaigns,” says Noreika. “That means staying on high alert for threats such as phishing, credential theft, account takeover attempts, denial-of-service-for-hire activity, and deepfake-enabled fraud, all of which can be scaled quickly and deployed with limited technical expertise.”

He recommends users and organizations re-evaluate their cybersecurity hygiene, ensuring that they use unique passwords for all accounts and don’t store them in built-in browser password managers, and that multi-factor authentication is enabled wherever possible. Software and systems should be kept up to date with the latest patches, and publicly available personal information should be kept to a minimum to reduce the material that attackers can use for social engineering or deepfake creation.

“If cybercriminals manage to get a hold of credentials or other sensitive information, it’s crucial to act as soon as possible,” says Noreika. “Deep and dark web monitoring can provide alerts of many instances of leaked data, allowing for the detection of leaks across both Telegram and multiple dark web forums. This visibility is key to initiating urgent responses — such as changing passwords, revoking access from compromised accounts, and staying on high alert for any signs of further escalation.”

Methodology: Nordayer Intelligence analyzed monthly post counts across dark web forums and Telegram channels monitored by the NordLayer Intelligence platform, covering seven popular cybercrime categories from January 2024 to May 2026. Between January 2024 and May 2026, 86 dark web forums and 1,890 Telegram channels were monitored. As new sources emerged and others were shut down or seized during this period, year-on-year comparisons reflect changes in activity alongside shifts in the source pool itself. “Share” refers to the average proportion of posts across the seven tracked cybercrime categories, calculated by measuring Telegram’s share of posts in each category separately and then averaging those figures. 2026 figures cover January–May only.

Findings are limited to NordLayer Intelligence’s monitored sources and are not representative of all activity on Telegram or the dark web. Post counts measure discussion volume, not confirmed criminal activity or victims. Only aggregate counts were analyzed; no personal user data was collected. For more information, visit NordLayer Intelligence’s blog post.

Disclaimer: This analysis is provided for general information only and does not constitute legal, security, or professional advice, nor any guarantee of security or outcome. It reflects activity detected within NordLayer Intelligence’s monitored sources during the stated period and describes aggregate patterns only – no conclusion is drawn about any identified individual or organisation. References to third-party platforms and services are for identification and factual reporting only and do not imply any wrongdoing by, endorsement by, or affiliation with those parties. All third-party trademarks remain the property of their respective owners.

The attacker had the password + MFA approval. Here’s why they still couldn’t get in

Posted in Commentary with tags on August 26, 2026 by itnerd

ReliaQuest/ShinyHunters. Let’s have a chat about this. Here’s what you need to know.

The attacker reportedly got the password and the MFA approval, and still couldn’t get where they wanted to go. MFA shouldn’t be the finish line for identity security. And device trust and conditional access can contain an attack even after an attacker gets through the front door.

The company put up a blog post here: https://reliaquest.com/blog/threat-spotlight-social-engineering-attempt-against-reliaquest-what-we-found/

Kevin Surace, CEO, Token (https://www.linkedin.com/in/ksurace)

“The ReliaQuest incident is a perfect example of why MFA can no longer be treated as proof of identity. The attacker reportedly obtained valid credentials and convinced the employee to approve the MFA request. At that point, the authentication system had effectively accepted the attacker as the employee. ReliaQuest’s additional device trust controls appear to have prevented that authenticated session from reaching critical applications, which is exactly why identity security has to extend beyond a password plus an approval prompt.

“The ultimate direction is dedicated hardware biometric assured identity. Instead of asking an employee to decide whether a push notification is legitimate, the system requires cryptographic proof from a registered physical authenticator, a biometric match from the authorized user, the correct application or domain, and ideally physical proximity to the device being accessed. There is no code to give away and no push notification to approve. Even if an attacker steals the password and completely fools the employee, they still cannot produce the required identity proof.

“That is where enterprise authentication is heading. Device trust is an excellent additional control, but dedicated biometric hardware moves the protection to the very beginning of the attack chain. Rather than detecting that the wrong device is being used after an attacker has already authenticated, biometric assured identity is designed to prevent the attacker from ever becoming an authenticated user in the first place. Attackers may steal credentials, call the help desk, or manipulate an employee, but without the authorized hardware and the authorized person, there is no entry.”

Noelle Murata, Chief Operating Officer, Xcape, Inc. (https://www.linkedin.com/in/nmurata)

“A compromised set of credentials or an approved multi-factor authentication (MFA) push does not have to result in a catastrophic breach when identity architectures enforce strict post-authentication boundaries. The bad news is that a user made a poor decision to approve the MFA push request; the good news is that the organization’s defense-in-depth posture worked as designed and prevented further unauthorized access. When threat actors bypass initial login protections to access an identity dashboard, downstream conditional access policies act as the true containment boundary. Single technical controls will eventually fail, making post-authentication conditional access essential for effective breach containment. Valid user credentials paired with approved MFA push requests should never grant unvetted access to downstream enterprise applications without device trust verification. Defense-in-depth strategies succeed when security architectures automatically isolate non-compliant or untrusted endpoints from core operational assets. This incident is a testament to how defenders can remain successful in preventing attacks if they assume that any single technical control can be bypassed. Security leaders must mandate managed device certificate validation, require hardware-bound security keys, and automatically isolate untrusted endpoints from core enterprise applications.

“Relying solely on human judgment for authentication is a strategy destined to fail, which is why real defense-in-depth ensures that failure stays contained.”

Jacob Krell, Sr. Director: Secure AI & Cybersecurity, Suzu Labs (https://www.linkedin.com/in/jacob-krell)

“Social engineering stops working when it runs into a gate that doesn’t involve a human. ShinyHunters got a valid password and an approved Multi-Factor Authentication (MFA) push from a ReliaQuest employee, and it still wasn’t enough to reach a single application. The session landed in Okta, the identity dashboard loaded, and device-trust controls blocked every attempt to go further because the attacker’s device wasn’t enrolled.

“ShinyHunters has made a career out of valid-looking access. Legitimate API calls against misconfigured Salesforce deployments. Stolen credentials against Snowflake customers. A phished MFA session against ReliaQuest. The first two turned into data breaches. The third didn’t, because device trust doesn’t care how legitimate your session looks.

“MFA push approval is a human decision, and social engineering targets human decisions. An attacker calls, creates urgency, and the employee taps “approve.” Device trust removes the human from that chain entirely. Conditional access policies that verify managed device certificates, Mobile Device Management (MDM) enrollment, or endpoint compliance are machine-to-machine checks.

“You can talk someone into approving a push notification. You can’t talk a laptop into passing a device compliance check.

“I’ve seen this with clients running Microsoft Entra ID. Phishing attempts that cleared MFA stopped dead at the device gate because the attacker’s machine wasn’t enrolled in the organization’s MDM. The credentials were valid, the session was live, and nothing happened. ReliaQuest’s Okta setup produced the same result.

“Too many organizations treat conditional access as a phase-two project they’ll configure after their identity migration finishes. This incident shows why it should be phase one.”

Basically the takeaway from this incident is that companies need to look at non-MFA solutions like passwordless solutions. That way companies are better protected from hacks like this.

New intelligent safety features coming to Volvo EX60 and EX90

Posted in Commentary with tags on August 26, 2026 by itnerd

Volvo Cars is introducing new Connected Safety features to alert drivers of hazards ahead, so they have more time to adapt and drive more safely. As part of the same software update, Volvo EX90 drivers will be able to enjoy Spatial Audio support in Apple CarPlay*, taking music and audio to the next level.

Pioneering safety features
First launched in 2016, Volvo Cars’ connected safety technology enables real-time hazard alerts based on data shared from other cars. The latest software update introduces four new alerts:

  • The Large Animal Alert can warn other drivers if a large animal is detected on or near the road ahead.
  • The Vulnerable Road User Alert can warn other drivers if pedestrians and cyclists are detected ahead on or near highways.
  • The Roadwork Alert can warn other drivers when roadwork is detected ahead.
  • The Accident Ahead Alert can warn other drivers of accidents further ahead, using real-time data from connected Volvo cars or traffic management centres.

Available in the Volvo EX90 and EX60, these features expand the system’s ability to provide clear, early warnings – especially in low-visibility conditions such as winding roads or poor weather. These complement existing features like the Slippery Road Alert and Hazard Light Alert.

Today, more than 1 million Volvo cars have activated connected safety tech, turning everyday journeys into a collective safety effort. Through the European Data for Road Safety ecosystem, the alert data can also be shared with cars from other brands and national traffic management centres, contributing to safer roads for everyone.

Enhanced audio experience
The latest software update also brings Spatial Audio support in CarPlay* to the Volvo EX90 with Dolby Atmos technology. Enabled by the Bowers & Wilkins premium sound system including 25 high-performance speakers, Volvo drivers can enjoy a multi-dimensional and immersive sound experience that places music and vocals around the cabin.

From a favourite track to a live performance or a podcast, Spatial Audio powered by Dolby Atmos adds depth and detail to everything you listen to – making every drive feel richer, more engaging and more enjoyable.

Volvo Cars was recently recognised by S&P Global Mobility as the only legacy carmaker to reach Level 5 capability in software-defined cars. The latest software update exemplifies how these vehicles continue to add safety features and become better over time.

The small print

  • The new connected safety features mentioned above will be available in Volvo EX60, EX90 and ES90 in Europe, US and Canada. Timing of availability may vary depending on car model.
  • Spatial Audio in CarPlay requires a Bowers & Wilkins sound system to deliver a fully immersive experience, which is available to choose when ordering the Volvo EX60, EX90 and ES90.

Norway DDoS attack exposes national resilience risks

Posted in Commentary with tags , on August 26, 2026 by itnerd

There have been a significant DDoS attack targeting Norway’s public services:

Norway ‘s shared digital government infrastructure has been hit by another distributed denial-of-service (DDoS) attack that disrupted services used by citizens, businesses and public agencies. The incident began at 03:38 CEST on Monday, August 24, and targeted infrastructure operated by the Norwegian Digitalisation Agency, Digdir, together with its service provider Vivicta. 

The timing matters because this isn’t an isolated event. Digdir says it’s the third DDoS attack against its services in a short period, following incidents in June and on August 3.

“The Norwegian Directorate for Digitalisation (Digdir) has been subjected to a denial of service attack (DDoS attack) that has been ongoing since 03:38 on the night of Monday, August 24.” reads the statement published by Digdir Agency. “This is the third time in a short time that this type of attack has been directed at Digdir’s solutions. Digdir is working closely with our subcontractor Vivicta. NSM and the Norwegian Data Protection Authority have also been notified of the case.”

That status update refers to the test environment, but the underlying attack also affected production services. Digdir reported that several shared services became completely unavailable for short periods, while others remained accessible but suffered connection failures, slow responses and longer-than-usual login times.

Kevin Surace, CEO, Token (https://www.linkedin.com/in/ksurace)

“This attack is a reminder that shared digital infrastructure can also mean shared failure. When a national identity service goes down, the impact can quickly spread across dozens of otherwise healthy government services.

“Organizations need to design for days of hostile traffic, not minutes – with redundant providers, upstream DDoS protection, geographic failover, and critical services that can degrade gracefully rather than simply disappear.

“At this scale, it stops being just an IT problem. If an attacker can prevent citizens from accessing essential government services, that is a national resilience issue. While attribution is not yet confirmed, the scale, persistence and target fit the pattern of Russian or pro-Russian disruption campaigns seen across Europe.

“Attackers don’t have to break into government systems to disrupt a country. Keeping people from getting in is enough.”

Doc McConnell, Head of Policy & Compliance, Finite State (https://www.linkedin.com/in/doc-mcconnell)

“A denial-of-service attack is often billed as a ‘cybersecurity’ incident, but the conversation about response should start with resilience, not security.

“The right measure of resilience is what a citizen can still do while the service is down. For some services, like filing a tax return, a delay of a day or two may be manageable. For others, like filling a prescription, a delay might not be acceptable. Organizations that depend on shared digital infrastructure need to understand which of their services can tolerate downtime and which can’t, then establish and regularly test the backups that keep life-, health-, and safety-critical functions running.

“There is a cybersecurity dimension to this as well. Although this incident hasn’t been attributed, attacks of this scale generally rely on large numbers of compromised IoT devices assembled into botnets: baby monitors, smart televisions, and home routers. These devices sell cheaply and in large numbers to buyers who have little reason to think about security updates, which leaves a large population of devices on the internet carrying exploitable vulnerabilities. That is where the capacity for large-scale DDoS comes from, and it is why connected device security matters well beyond the owner of any one device.

“Manufacturers are the party best positioned to reduce that supply, and two priorities matter most: shipping products that are secure by default, out of the box, and maintaining a way to deliver security updates for as long as the product is in service.” 

Damon Small, Board Member, Xcape, Inc. (https://www.linkedin.com/in/damon-small-7400501)

“Centralization buys efficiency in peacetime and pays for it in a crisis; the same architecture that made ID-porten convenient made a single operational disruption a national outage. When one digital bottleneck can freeze transit, medical access, and government data at once, cybersecurity stops being server defense and becomes national security. While a distributed denial-of-service attack does not compromise underlying data integrity, a prolonged multi-day surge highlights the operational fragility of shared authentication backbones. The common thread is redundancy before the outage, not response after it; implement distributed identity, always-on filtering, and shared accountability for the auth layer. To ride out sustained Layer 4 and Layer 7 flooding without triggering cascading service collapse, security leaders must decouple non-critical dependencies, deploy automated edge scrubbers with multi-provider content delivery networks, and implement graceful degradation paths so localized outages do not paralyze civil infrastructure.

“Critical takeaways include: single points of failure in centralized identity infrastructure elevate volumetric network attacks from IT disruptions to national security crises; operational resilience requires pre-outage architectural investments, including distributed identity backbones and multi-provider traffic scrubbing; and critical infrastructure must support graceful degradation paths so that identity layer outages do not halt core civil and municipal operations.

“Redundancy built before the storm is resilience; redundancy attempted during the attack is just panic.” 

Denis Calderone, Principal & COO, Suzu Labs (https://www.linkedin.com/in/deniscalderone)

“There are legitimate reasons to funnel an entire country’s public services through a single authentication gateway. You get one place to enforce policy, one set of logs to monitor, one surface to harden. The tradeoff is obvious though: that single entry point becomes the one thing you absolutely cannot let go down. And if you’ve made that architectural choice, you’d better have every DDoS defense in the book tuned and tested for that exact chokepoint.

“Three attacks in nine weeks against the same vendor, the same infrastructure, with 30-plus hour outages each time. That tells me the defenses either weren’t there or weren’t scaled to match the criticality of what they’re protecting. When your mitigation strategy is geo-blocking entire countries’ worth of IP space after the attack is already underway, you’re doing reactive triage, not DDoS defense. Upstream scrubbing, anycast distribution, automated traffic diversion to cleaning centers, pre-negotiated capacity with mitigation providers, all of that should be standing and warm before the first packet of attack traffic arrives. You don’t build the levee during the flood. And you certainly don’t build the same inadequate levee three times in a row. When pharmacies can’t fill prescriptions and health systems go dark because one vendor’s network is getting flooded, that’s not an IT availability problem anymore. That’s a failure to treat critical national infrastructure like critical national infrastructure.”

I know that I’ve said it before. You need to sort your stuff out so that you’re defended against these attacks. Or you will be the next victim of these attacks. It’s that simple.

The CISA orders federal agencies to patch actively exploited Oracle flaw by August 27

Posted in Commentary with tags on August 25, 2026 by itnerd

The CISA has added a maximum-severity Oracle vulnerability, CVE-2026-21962, to its Known Exploited Vulnerabilities catalog after confirming active exploitation.

The flaw carries a CVSS score of 10.0 and affects Oracle HTTP Server and the Oracle WebLogic Server Proxy Plug-in for Apache HTTP Server and IIS.

The vulnerability can be exploited remotely over HTTP without authentication or valid credentials, potentially allowing attackers to access, modify or delete critical data.

Oracle originally disclosed and patched CVE-2026-21962 on January 20, 2026, as part of its January Critical Patch Update. In March, researchers reported exploitation attempts after exploit code became publicly available.

CISA has ordered federal agencies to address the vulnerability by August 27.

Jacob Krell, Senior Director: Secure AI Solutions & Cybersecurity, Suzu Labs Had This To Say:

   “CVE-2026-21962 had a patch on January 20, and CloudSEK recorded exploitation attempts against its honeypot on January 22, followed by broader automated scanning. CISA added it to the KEV catalog on August 24, 216 days after the patch. Federal agencies now have three days to remediate something attackers have had seven months to exploit.

   “In January, agencies could have applied the Critical Patch Update inside a normal maintenance window and moved on. Seven months of delay while exploitation attempts and automated scanning were already being observed from rented VPS infrastructure changed the math. BOD 26-04 requires forensic triage at this severity tier, so agencies now have to assess whether compromise occurred during that seven-month exposure period alongside applying the patch.

   “BOD 26-04’s 16-tier remediation matrix is well-designed for the problem it solves. For a vulnerability in the KEV, automatable, and yielding total control of a public-facing asset, the clock is three days with forensic triage. In this case, CISA’s August 24 KEV addition produced an August 27 federal remediation deadline, while CISA’s obligation is to update the catalog “as quickly as possible,” with no numerical SLA. EPSS ranked this in the top 1.4%, Shodan shows roughly 79,000 exposed Oracle HTTP Server instances, and CISA’s own SSVC record dates active exploitation to January 21 while classifying the vulnerability as automatable with total technical impact.

   “Three days to remediate is the right call. Seven months to trigger it turned a maintenance window into a forensic investigation.”

This of course means update all the things ASAP. But we’re getting to a point where patching anything is a losing battle. Thus we need to think of something new when this avenue exhausts itself.

UPDATE: Also Commenting on this is Dan Moore, Sr. Director, CIAM Strategy & Identity Standards at FusionAuth: 

“The thousands of organizations relying on Oracle WebLogic to provide secure access to their applications are at risk of data loss, manipulation, and exfiltration. The unauthenticated access allows an attacker to make application calls to read data, as well as insert their own unauthorized changes. This issue affects any server accessible to an attacker, which is extremely problematic for many internet exposed applications.”